Email Security
Customer Stories
Lokker + AegisAI - Customer Story
Learn how Lokker thwarts attacks seamlessly while reducing overhead for their security team.


Lokker, founded in 2020 and headquartered in San Francisco, CA, offers Privacy Edge™, a SaaS platform that protects corporate websites and customers from unauthorized data capture, trackers, and privacy threats. With a mission to "power privacy" and limit data collection to what’s essential, Lokker empowers marketing, engineering, and legal teams to enforce compliance while safeguarding user data.
Given Lokker’s strong focus on privacy, operational security, and minimizing data retention, security was at the forefront of CEO Ian Cohen’s mind. Formerly, Ian served as General Manager and Chief Product Officer at Experian’s Consumer Services Division. Prior to Experian, he served as Chief Executive Officer of Credit.com from 2009-2015. Ian knew Lokker’s email communication systems—central to client interactions and vendor coordination—needed robust protection against phishing, BEC (Business Email Compromise), Malware, and other advanced email threats without blocking legitimate emails.
Like many tech and privacy-focused companies, Lokker confronted growing threats targeting their organization:
Over time Ian and the Lokker team had seen a rapid spike in these attacks. They’d also noticed an increase in sophistication. Attackers using AI to target specific employees as well as rotation of attack patterns designed to evade detection rules. They needed a zero-hassle tool that could evolve and react to the most modern threats. Furthermore, AegisAI’s data minimization architecture aligns with Lokker’s principles—only suspicious content is retained for optional review.
AegisAI was simple to integrate via API with their Google Workspace account, enabling instant scanning of inbound and outbound mail, a 5 minute task handled on a call.
“I thought I was going to have to spend a lot of time on these suppression lists, and we didn’t…I’m pretty thrilled about that”. Ian Cohen, CEO, Lokker
Lokker’s deployment of AegisAI followed a streamlined plan:
The team ran Aegis in monitoring/silent mode for two weeks, generating no user-facing actions—this gathered insight on typical mail flows and allowed tuning of incident workflows. They found early on that their current phishing protection solution was missing several attacks that remained in user inboxes weeks later. Upon validation, AegisAI shifted to active blocking mode—quarantining threats, stripping malicious attachments, and tagging risky emails.
0 phishing attacks reported by employees
0 escalations due to false alerts
0 maintenance cost
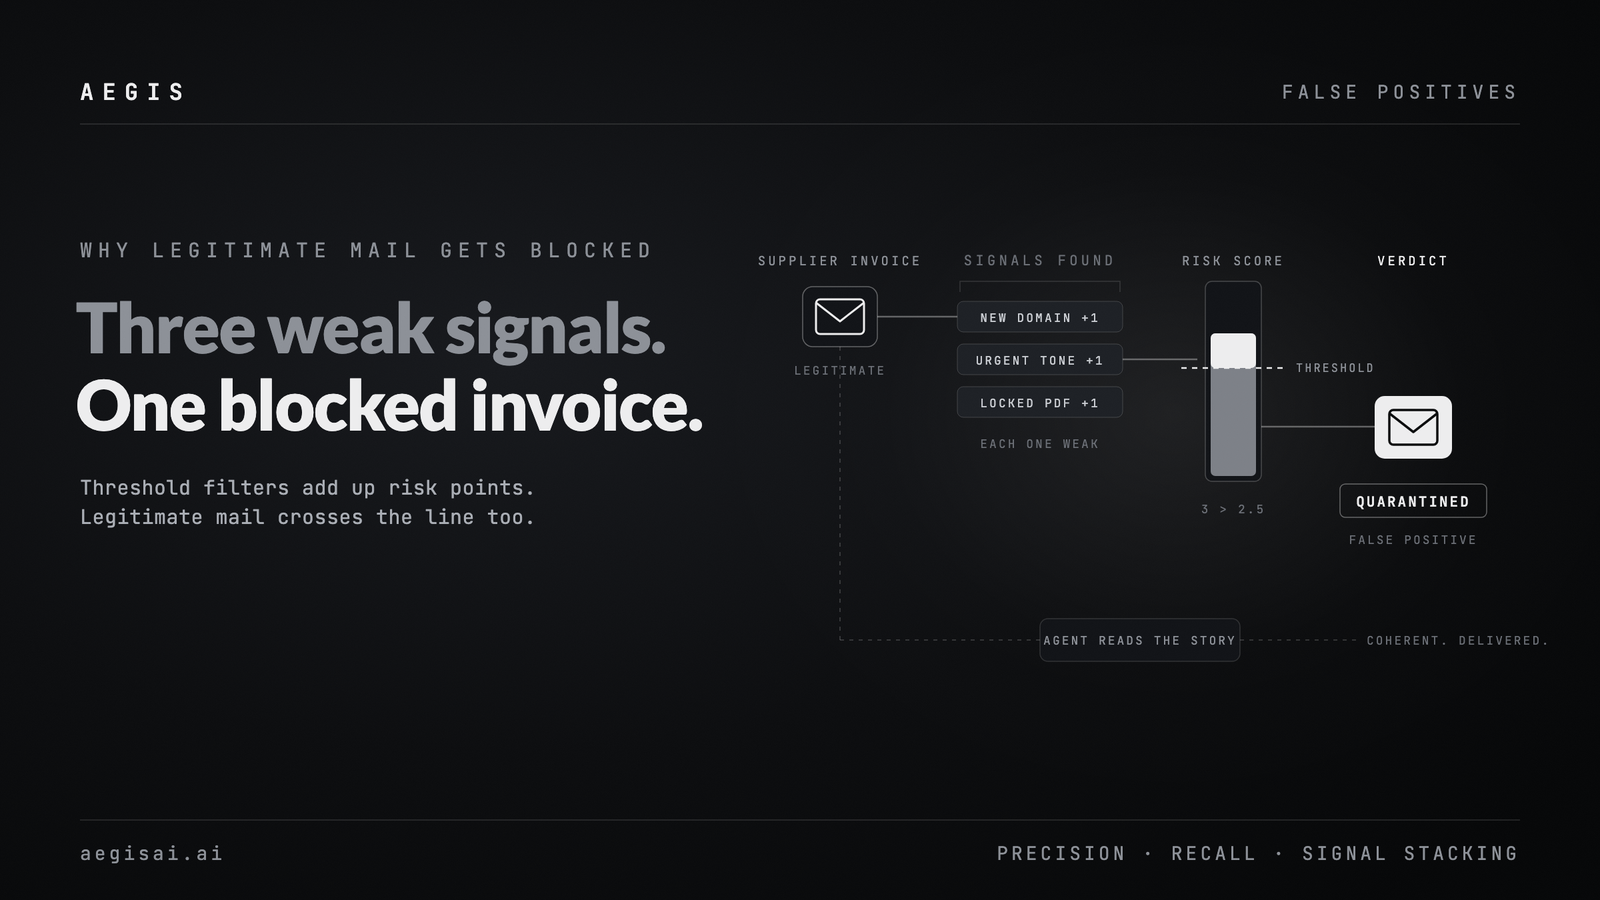
Over the first quarter of live deployment the Lokker team was able to see that the majority of their employees were being targeted by 100+ attacks that were making it past their existing email security solution. However, with Aegis none of them were making their way through.
“We immediately saw threats to our accounting, engineering, and executives teams in the dashboard. Aegis enabled us to see and stop these threats without our team manually hunting them down.”
Even when salesforce.com was compromised to send phishing attacks to Lokker’s CRM team, Aegis caught it. Aegis offered consistent real-time protection—no rule tuning required. Aegis Agents adapted to zero-day threats instantly.

AegisAI helped Lokker deliver on its core promise: protecting user privacy without compromise. By seamlessly securing Lokker’s email systems, AegisAI eliminated a major attack surface—without adding overhead for the security team. This allowed Lokker to stay focused on proactive threat hunting while knowing their inboxes were fully protected.
What truly stood out were AegisAI’s explainable, human-readable alerts. These not only stopped sophisticated phishing attempts but also helped Lokker educate employees on evolving social engineering tactics—transforming them into a stronger line of defense. The result? Enhanced security posture, reduced data risk, and continued alignment with Lokker’s mission to safeguard privacy with enterprise-grade rigor.